Research · Generative & Agentic AI
AI Agents & Multi-Agent Systems
AI agents plan and carry out multi-step tasks by calling tools and applications. Multi-agent systems divide work among several specialized agents. Both can automate work that used to need a person, and both need strong controls.
The Bounded Agent Stack
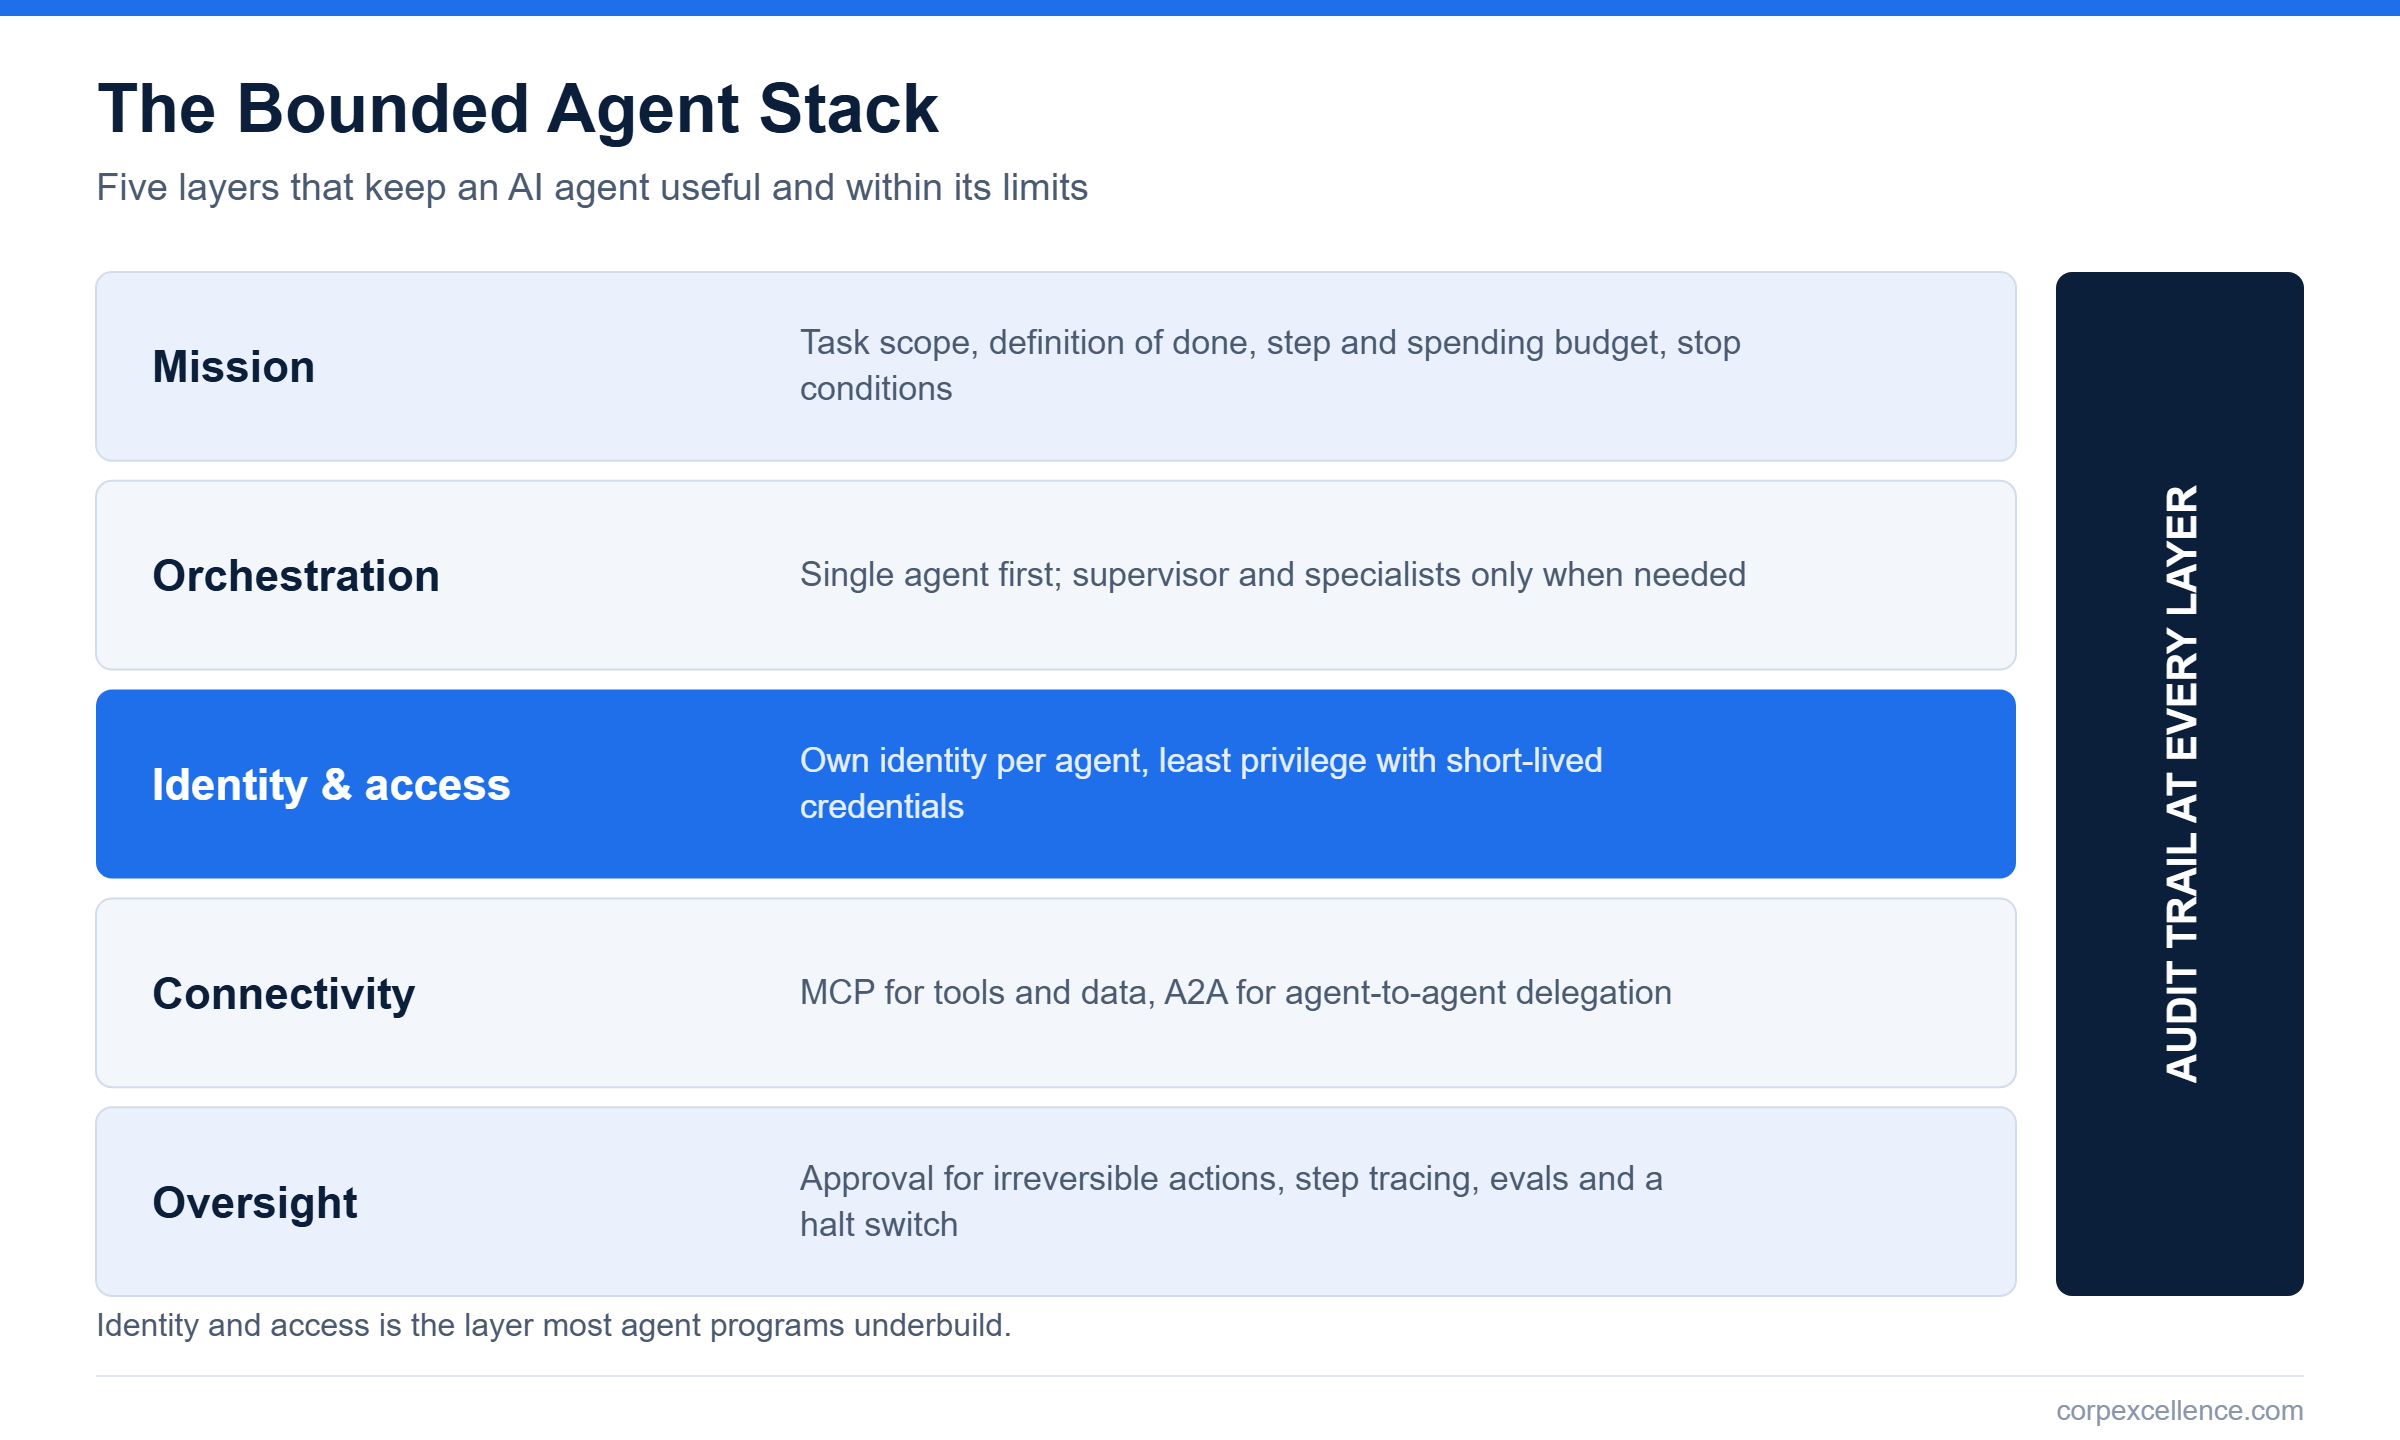
An AI agent is a model that plans and takes actions through tools until a goal is met. Multi-agent systems split that work across specialized agents that hand tasks to one another. Risk grows with each tool an agent can call and each agent it can delegate to. The Bounded Agent Stack, a CorpExcellence framework, describes five layers every production agent needs, with an audit trail running through all of them.
Mission and orchestration
The mission layer defines what the agent is for: the task scope, what counts as done, a spending or step budget, and the conditions that stop a run. Vague missions produce agents that wander. The orchestration layer decides structure. Start with a single agent and a short list of tools. Add a supervisor with specialist agents only when one agent’s context or tool list grows too large to manage, because each handoff adds a point where errors compound.
Governing agents that act inside your systems?
Governing Agentic AI 2026 sets autonomy per action class with the A0 to A5 Agent Autonomy Scale and organizes controls into six planes, from agent identity and MCP connectivity to oversight and kill switches.
Identity and access
This is the layer most programs underbuild. Give every agent its own identity rather than a shared service account or a borrowed user session. Grant least privilege with short-lived credentials, and keep read access separate from write access. When an agent acts for a user, record both identities. NIST’s AI Agent Standards Initiative, launched in February 2026, includes agent identity and authorization in its work.
Connectivity
Two open protocols now cover most agent connections. The Model Context Protocol (MCP) connects an agent to tools and data. Agent2Agent (A2A) lets independent agents discover each other and delegate tasks across vendors. Both sit in the Linux Foundation’s Agentic AI Foundation: MCP since the foundation launched in December 2025, and A2A since it was accepted as a project in August 2026. A2A matters most when agents from different vendors need to cooperate. Treat every MCP server as third-party software. Review it and pin its version before any agent can use it.
Oversight
Require human approval before irreversible actions such as payments or external messages. Trace every step, including tool calls and the content the agent read, so you can reconstruct why it acted. Test agents against realistic tasks and prompt injection attempts before release, and keep a way to halt them in production. Set alerts for unusual behavior, such as a spike in tool calls or access to data outside the mission.
One agent task can become a long chain of model calls
AI Inference Cost Control shows how to measure the agentic cost multiplier and bound it with limits on steps, retries, tool calls and cost per task.
Where the industry is now
As of September 2026, the protocol layer is consolidating under neutral governance and security guidance is catching up. OWASP published its Top 10 for Agentic Applications in December 2025, and NIST has sought public input on agent security and on agent identity and authorization. Formal agent standards are still in development, so build controls now that you can map to them later.
Common pitfalls
- Running agents on a human user’s full permissions.
- Adding agents to a workflow before a single agent works reliably.
- Connecting unreviewed MCP servers from public directories.
- Logging final outputs but not the steps that produced them.
Research report
Keep agent costs bounded as you scale
Get the 52-page playbook with agent cost controls, a model routing policy template, anomaly guardrails and a governance control catalog for AI spending.
Featured research report
Governing Agentic AI 2026
67-page playbook for governing enterprise AI agents: autonomy levels, risk tiers, agent identity, MCP controls and human oversight. Includes 10 ready-to-use templates.
Featured research report
AI Inference Cost Control
52-page FinOps playbook for production AI. Includes a cost-per-transaction worksheet, a model routing policy template and an AI spending governance control catalog.
Questions leaders should ask
- What can each of our agents do without human approval?
- Does each agent have its own identity and minimum permissions?
- Can we reconstruct exactly what an agent did and why?
- Who is accountable when an agent makes a mistake?
More in Generative & Agentic AI
Related research reports
In-depth reports with ready-to-use templates.
- Governing Agentic AI 2026$59.99 PDF report
- AI Inference Cost Control$49.99 PDF report
Related research reports
Reports connected to this topic.