Research
AI Security
AI creates new attack surfaces and gives attackers new tools. This area covers securing AI systems, the AI supply chain, deepfakes and AI-enabled fraud, and the use of AI in security operations.
Topics in AI Security
Securing AI Systems (prompt injection, data poisoning)
Defending models, prompts, data and agents from attack.
Deepfakes & AI-Enabled Fraud
Countering synthetic media and AI-assisted social engineering.
Overview
AI systems can be manipulated in ways traditional software cannot. Prompt injection can redirect a model through hidden instructions, poisoned data can corrupt what a model learns, and agents with broad permissions can be turned against the systems they serve. Resources such as the OWASP Top 10 for Large Language Model Applications and MITRE ATLAS catalog these threats.
At the same time, attackers use generative AI to produce convincing phishing, synthetic voices and deepfake video. Defenders are also adopting AI to triage alerts and investigate incidents faster.
What leaders need to get right
- Threat modeling. Include AI-specific attacks in security design reviews.
- Least privilege. Treat models and agents as identities with minimal access.
- Supply chain. Know where models, data sets and AI libraries come from.
- Verification. Update payment and approval processes so a convincing voice or video is never enough.
Research report
Agents are a new class of identity and attack surface
Governing Agentic AI 2026 covers agent identity, MCP and A2A connectivity, prompt injection, runtime limits, kill switches and incident response, with a tool and MCP server intake review.
Featured research report
Governing Agentic AI 2026
67-page playbook for governing enterprise AI agents: autonomy levels, risk tiers, agent identity, MCP controls and human oversight. Includes 10 ready-to-use templates.
Questions leaders should ask
- Have our AI applications been tested for prompt injection?
- Do we know the origin of every model and data set we use?
- Could a deepfake of an executive trigger a payment in our organization?
- Where is AI helping our security team, and how is it supervised?
Other research areas
Related research reports
In-depth reports with ready-to-use templates.
- Governing Agentic AI 2026$59.99 PDF report
- Third-Party AI Risk$59.99 PDF report
Related research reports
Reports connected to this topic.
Latest insights on AI Security
Agentic Autofix ROI: How to Measure Fix Quality, Review Work, and Regressions
Agentic security remediation should be judged by verified risk reduction per unit of engineering effort—not by the number of pull requests an AI agent opens. A proposed fix only creates [...]
From Cloud Compromise to Credential Harvesting in Under Six Hours: A Defensive Playbook
A documented 2026 agent-enabled attack compressed credential harvesting into hours. Defensive controls for cloud identities, detection and practiced containment.
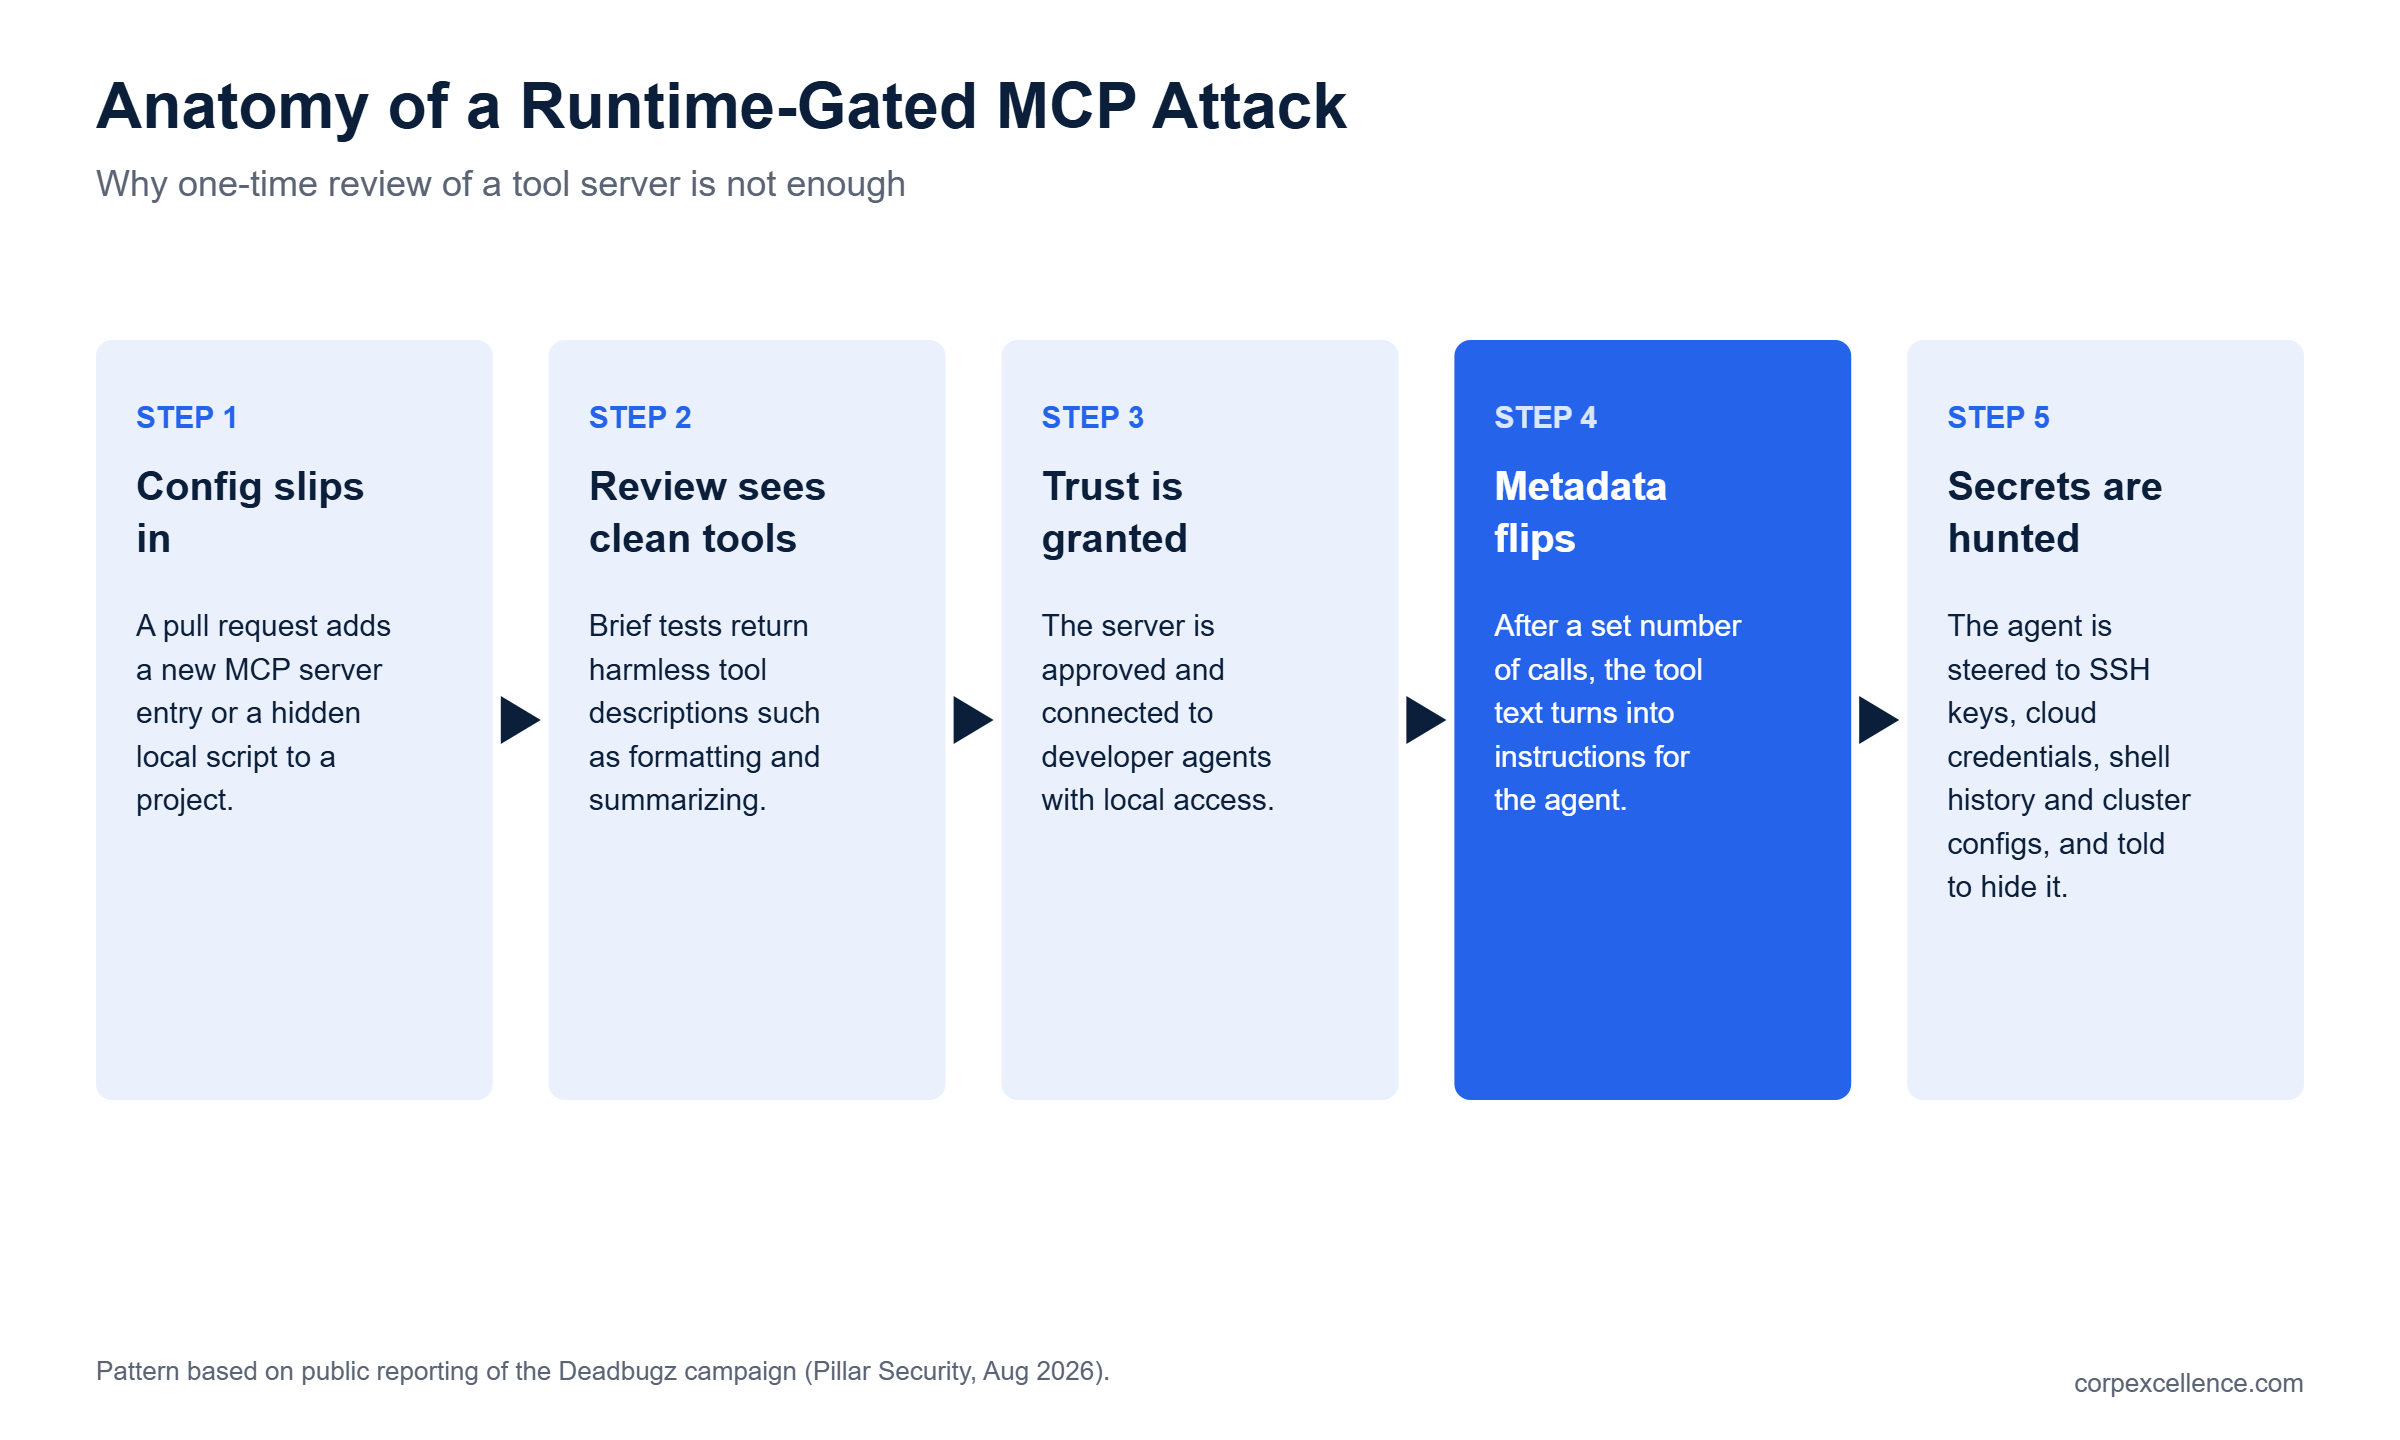
Deadbugz and the MCP Supply Chain: How to Stop Malicious Tools From Hijacking AI Agents
A malicious MCP server that behaves well until it is trusted. What the August 2026 Deadbugz campaign teaches security leaders about the AI agent supply chain, and five controls to put in place.